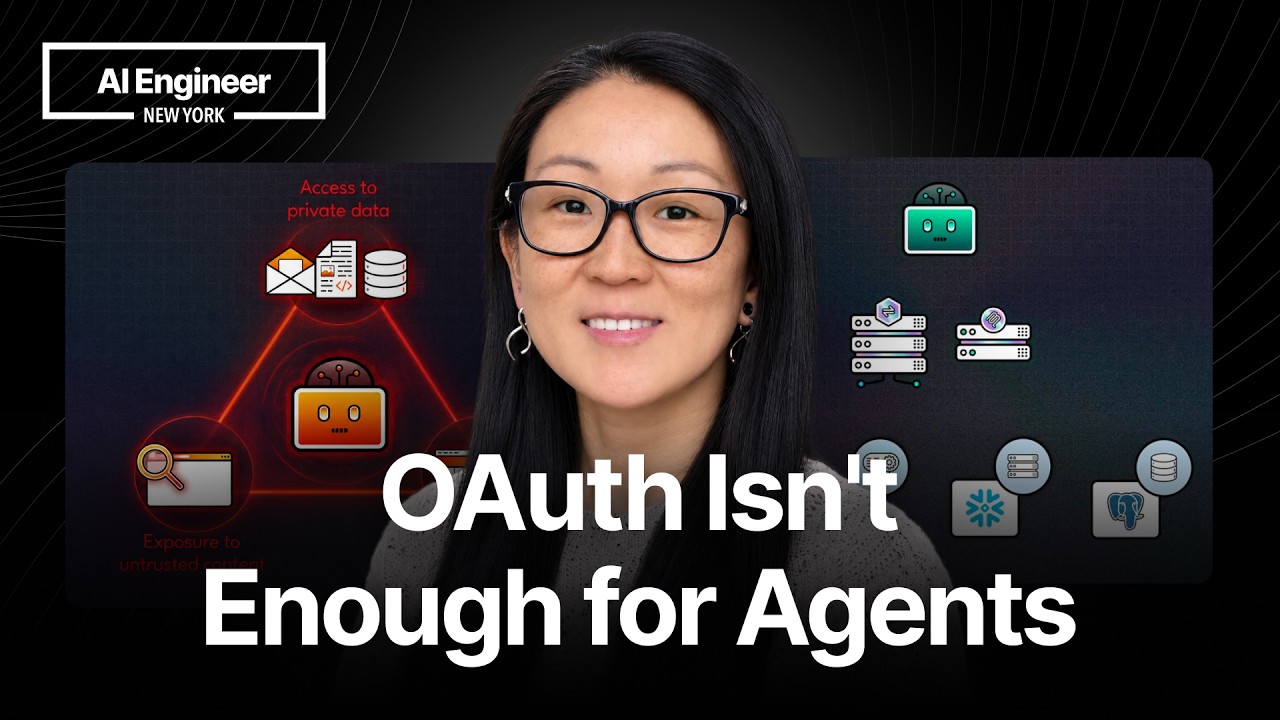
Your Agent Is a Lethal Trifecta (And What to Do About It) — Kim Maida, Keycard
The video addresses the security risks posed by overprivileged AI agents, which combine access to private data, exposure to untrusted content, and external communication capabilities—the 'lethal trifecta.' The solution presented moves beyond traditional access control methods (like OAuth or sandboxes) by implementing delegated authorization using OAuth token exchange. This process ensures that agents receive short-lived, task-scoped credentials, making identity, policy, and access decisions visible throughout the entire request chain.
Key takeaways
-
The Lethal Trifecta
6:56
AI agents are dangerous because they combine access to private data (e.g., customer data warehouse, billing database), exposure to untrusted content (e.g., user-submitted tickets), and external communication capabilities (e.g., third-party APIs). Overprivileged agents can execute catastrophic actions (e.g., dropping a production database, scaling services) even with human supervision. (4:16, 2:32)
-
Delegated Authorization via Token Exchange
14:03
To mitigate risk, the system must use OAuth token exchange, which extends OAuth 2.0. This process ensures that the user's identity is carried through the agent execution path, allowing the Security Token Service (STS) to evaluate policy and issue credentials scoped only to the specific, requested task. (8:43, 12:18)
-
Intent-Based Authorization (IBA)
23:31
IBA is a proposed standard (not finalized) that checks the user's intent or 'mission' before the agent acts. The STS evaluates the proposed mission (goal, allowed actions, limits) against policy, ensuring the agent cannot perform actions outside the defined scope, even if the underlying API key has broad permissions. (14:11)